A software supply chain with one place to block
Teams on npm, Go, PyPI, Maven, and NuGet, each pulling packages from a source of its own.
- place to block a vulnerable version, instead of one per source
- 1
- gates against a tampered package: the hub holds it, and admission would refuse it
- 2
The problem
Each team resolved packages from the public registry, its own mirror or a vendored copy. Blocking a vulnerable version meant going source by source.
What I changed
I centralized resolution into a hub, Nexus, and decommissioned the other sources. The hub became one service of an internal development platform (IDP): publishing goes only through the pipeline, with an attested, signed build and a scan in OWASP Dependency-Track. On the other end, a consuming build admits a package only if its signature and attestation verify.
How it works
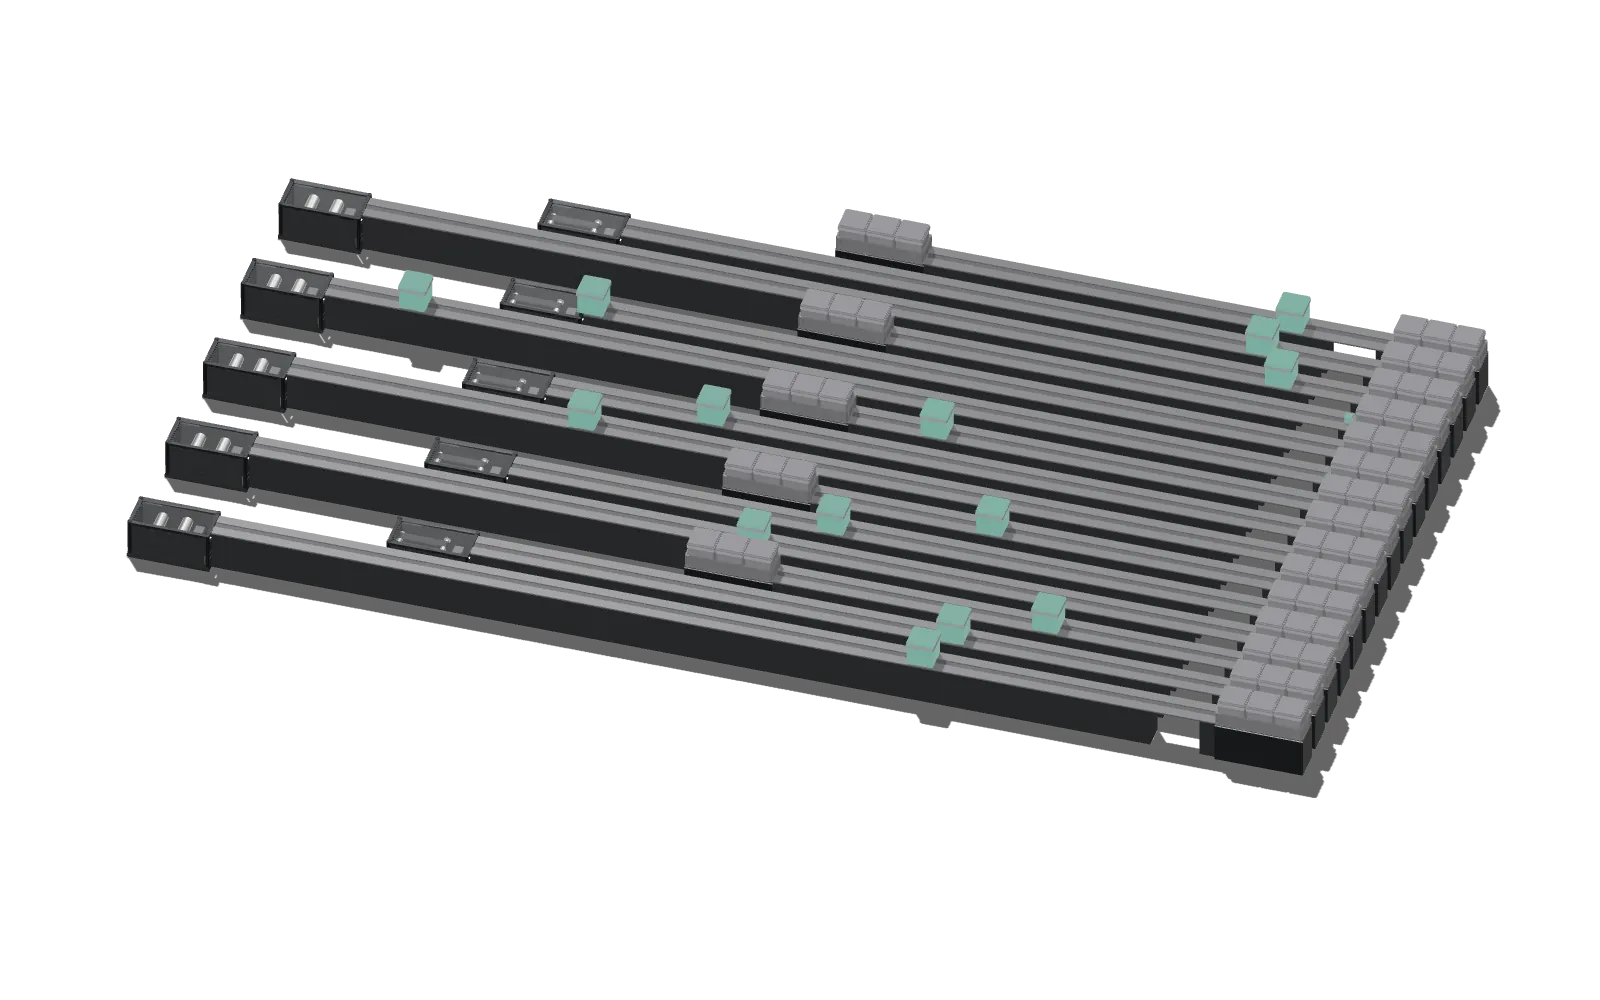
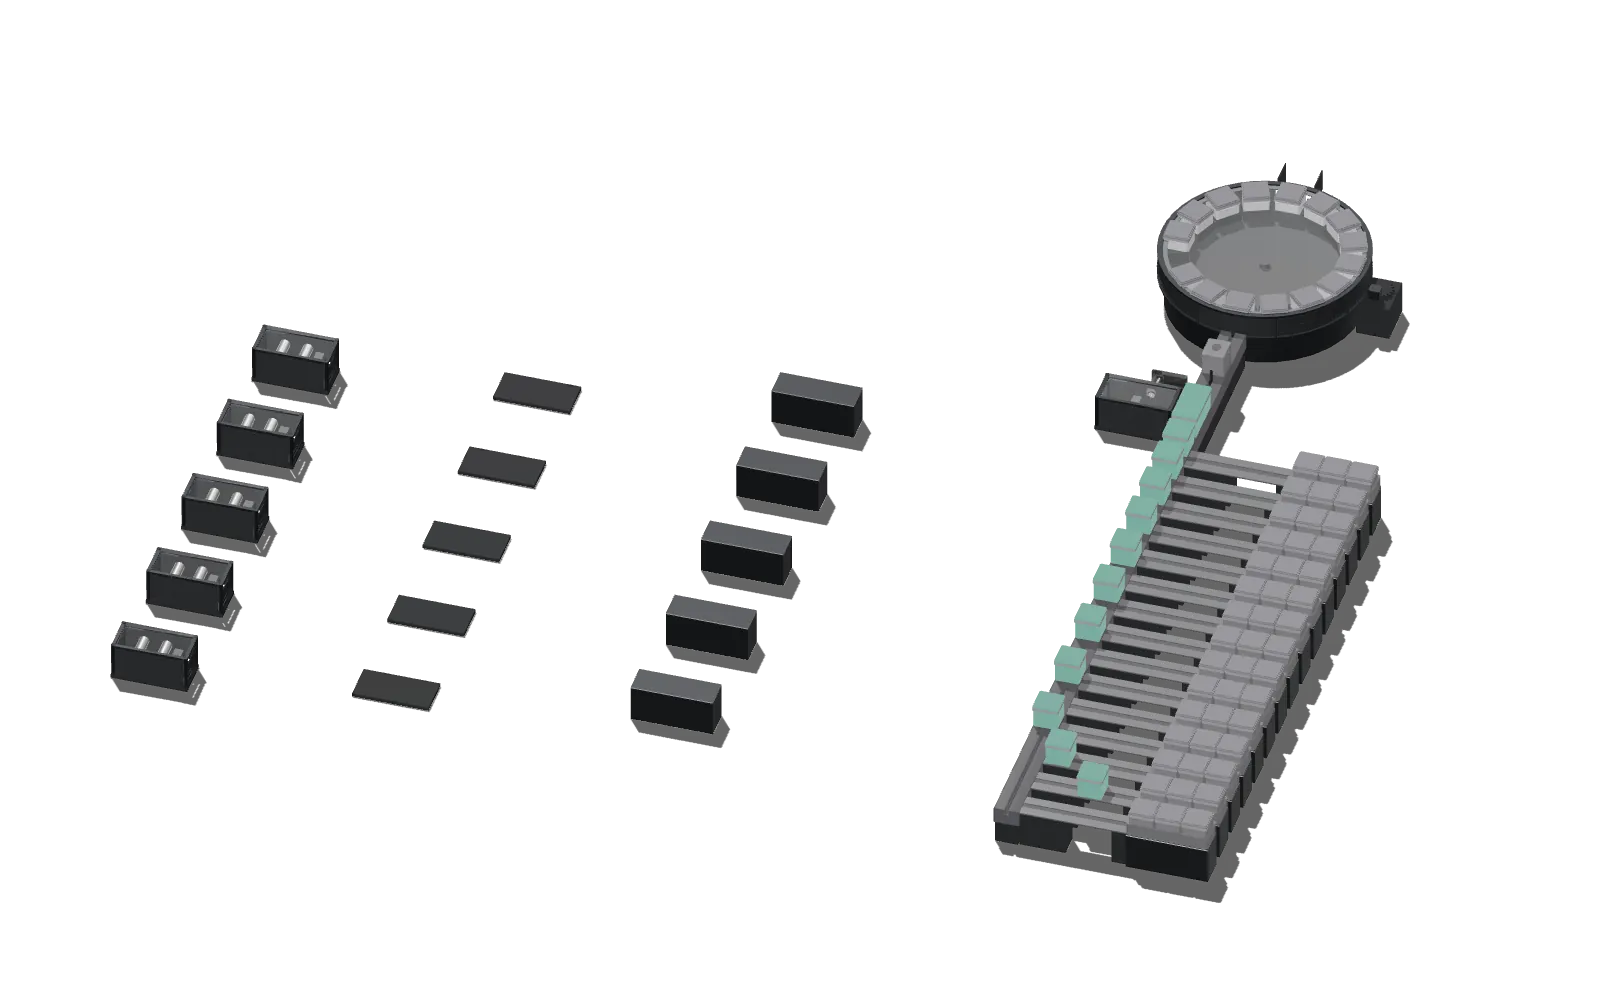
The parameters
- Ecosystems
- 5 ecosystems
- Teams per ecosystem (n)
- 3 teams
- Block at one place (B)
- 2 h
- Attested build
- 0.5 h
- Scan
- 0.25 h
The rules
places     before = n   after = 1
window     places · B
published  ⇔ attestation ∧ OIDC identity = pipeline ∧ digest = attested digest ∧ violations = 0
admitted   ⇔ the pipeline’s signature over the digest ∧ the pipeline’s attestation over the digest
Want one place to block what should not get in? Let’s talk.